Compliant AI and software for regulated industries
We build GDPR and EU AI Act compliant AI systems, speech-to-text pipelines and software for your team. Data protection, auditability and human oversight shape the architecture from the start.
- Based in
- Málaga, Spain
- Hosting
- EU-only or on-prem
- Built for
- GDPR · EU AI Act
- Languages
- EN · ES · UK · RU
- Avg. reply
- < 4 business hours
- First scope
- ~5 days
Services
Four services, one compliance baseline
AI and regulatory compliance are our focus. We build LLM systems, transcription pipelines, platforms and websites with the data protection and security your project needs.
Compliant LLM development
Assistants that retrieve your documents, respect access permissions and cite their sources.
Learn moreSpeech-to-text pipelines
Live or batch transcription that separates speakers, redacts as it goes and can run entirely on your own hardware.
Learn moreCustom platform development
Internal tools, admin panels, data workbenches and multi-tenant SaaS, shaped around how your team really works.
Learn moreWebsite development
Multilingual websites with clear content, accessible navigation and technical SEO.
Learn moreSelected results
Projects we have built
Each case study covers the problem, what we built and what changed afterwards.
VitalGen · Healthcare · 2026
VitalGen: speech-to-text for clinical documentation
We designed and built VitalGen to capture consultation speech and prepare structured notes for clinician review, with a target of reducing administrative work.
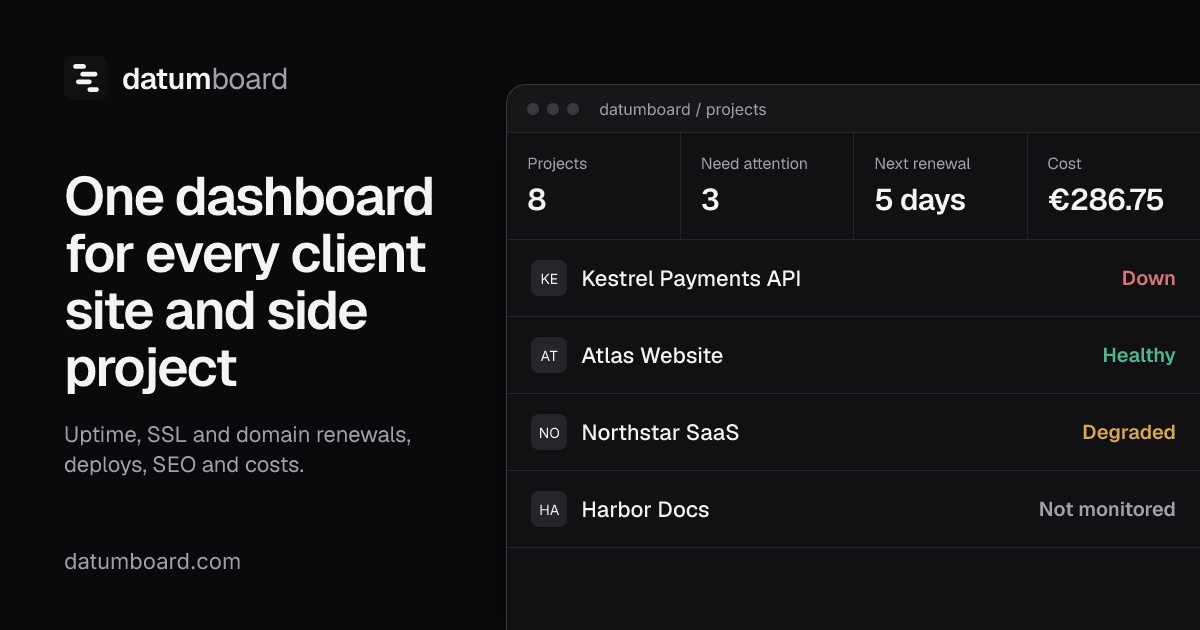
Datumboard · SaaS · 2026
Datumboard: our own dashboard for client sites and side projects
LoopClub · Consumer app · 2026
LoopClub: our women-only app for making friends in Buenos Aires
Milestone Expert SL · Construction · 2025
Milestone Performance: a multilingual, SEO-ready website for a construction company


Industries
Software for your sector’s workflows
Healthcare
Clinical documentation and patient-data workflows with access controls, defined hosting and clinician review.
Public sector
CMS-driven sites and internal tools for municipalities and other public bodies.
Education
Lesson recording, summaries and study tools for students and institutions.
Construction & real estate
Websites that explain your services, show completed work and help clients contact you.
Digital products & startups
Product interfaces and launch websites that explain your app, its features and the next step for users.
Security & compliance
What every project starts with
We follow GDPR and EU AI Act requirements from the first architecture decisions. We document and test the data protection, access and oversight controls your system needs.
Hosting defined for your data
EU-hosted or on-premises deployment, with processing locations and vendor access defined in your scope.
Personal data gets masked
We detect and mask personal details the task does not need, and test for missed values.
Audit logs with limits
We define which events to log, who can read them and when to delete them.
Role-based access
Roles, permissions and internal boundaries, enforced across the whole system.
Encrypted by default
We define encryption for stored data and data in transit in the architecture.
A person stays in the loop
Review and approval steps wherever AI output affects people.
How we work
From first call to go-live
- Step 1
Discovery call
A 30-minute call about your workflow, data and constraints. We reply to enquiries within four business hours, Málaga time.
- Step 2
Scope & architecture
You usually receive a scope and architecture document in about five days, including the compliance approach and a fixed estimate.
- Step 3
Build in increments
We deliver working software in two-week increments so you can review progress and test the workflow.
- Step 4
Launch & handover
Production release, documentation, audit-log access and the full code. It's yours.
Guides
Recent from the blog
GDPR-compliant LLM: how to choose a model and host it in the EU under GDPR and the AI Act
No language model is GDPR compliant on its own, because compliance depends on where it runs, who operates it, what contract covers it and what data you send.
 Artem Synytskyi·
Is your AI system high-risk under the EU AI Act? How to classify it in four steps
An AI system is high-risk if it is a safety component of a regulated product or serves an Annex III purpose such as hiring or credit scoring, unless a narrow Article 6(3) exception applies.
Artem Synytskyi·EU AI Act and emotion recognition from voice: what is banned, what is high-risk and how it is enforced
The AI Act bans biometric emotion inference in workplaces and education, except for medical or safety reasons, and sets further rules for other uses.
 Erik Salo Akimov·
FAQ
Frequently asked questions
ESADEX is a software and AI company in Málaga, Spain. We build GDPR and EU AI Act compliant LLM systems, transcription pipelines, platforms and websites for regulated industries.
Build your compliant AI or software project
Tell us your workflow and compliance requirements. We reply within four business hours and usually prepare a scope and architecture document in about five days.